MD5 (Message-Digest algortihm 5) is cryptographic hash function to wide according to hash value 128-bit. The internet standart (RFC 1321), MD5 use do all sorts of things in secure applications, and MD5 use also to exam integrity a bundle.
okeyy...let's go to practices :
1. open terminal
2. type in terminal 'findmyhash MD5 -h teks_md5' > enter'
Happy Hacking
Daftar Blog Saya
Senin, 31 Agustus 2015
Selasa, 11 Agustus 2015
Cracking Password Winrar
We frequently use zipped files due to its small size and strong
encryption algorithm. These zipped files comes with a facility of
password protection which maintains the security of the files.
But sometimes this security feature turns into a drawback if we somehow forget the password. In that case the password cracker play their role. You can also use them if you downloaded a zipped file with password protection on it.
In my last article, if you followed then we learned to make a bootable USB of backtrack. So here I'm gonna introduce a tool which is present in Backtrack and if you have no past experience with Linux then no issues you can start from here. The open source tool we are gonna use is called fcrackzip.
fcrackzip is a fast password cracker partly written in assembler. It is able to crack password protected zip files with brute force or dictionary based attacks, optionally testing with unzip its results.
But sometimes this security feature turns into a drawback if we somehow forget the password. In that case the password cracker play their role. You can also use them if you downloaded a zipped file with password protection on it.
In my last article, if you followed then we learned to make a bootable USB of backtrack. So here I'm gonna introduce a tool which is present in Backtrack and if you have no past experience with Linux then no issues you can start from here. The open source tool we are gonna use is called fcrackzip.
fcrackzip is a fast password cracker partly written in assembler. It is able to crack password protected zip files with brute force or dictionary based attacks, optionally testing with unzip its results.
Rabu, 29 Juli 2015
SQL injection
SQL Injection merupakan cara hack website yang paling banyak digunakan oleh para hacker. Kenapa? Karena dengan melakukan SQL injection, kita dapat langsung mengetahui username dan password dari website
yang akan kita bajak. Kok bisa gitu? Kasih tau gak yah? hehe, ya udah
siapin kopi dulu sana terus lanjut bacanya karena untuk melakukan teknik
ini dibutuhkan kesabaran ekstra,hehe..
Rabu, 04 Februari 2015
I Delete a Blog on Blogger
Today many blogs that allow users neglected blog. Various preoccupations of bloggers so just let his blog. Of course this is very detrimental to the new blog users because the number of blog address they like no / reduced.
Here's how to remove an abandoned blog
Good luck ....
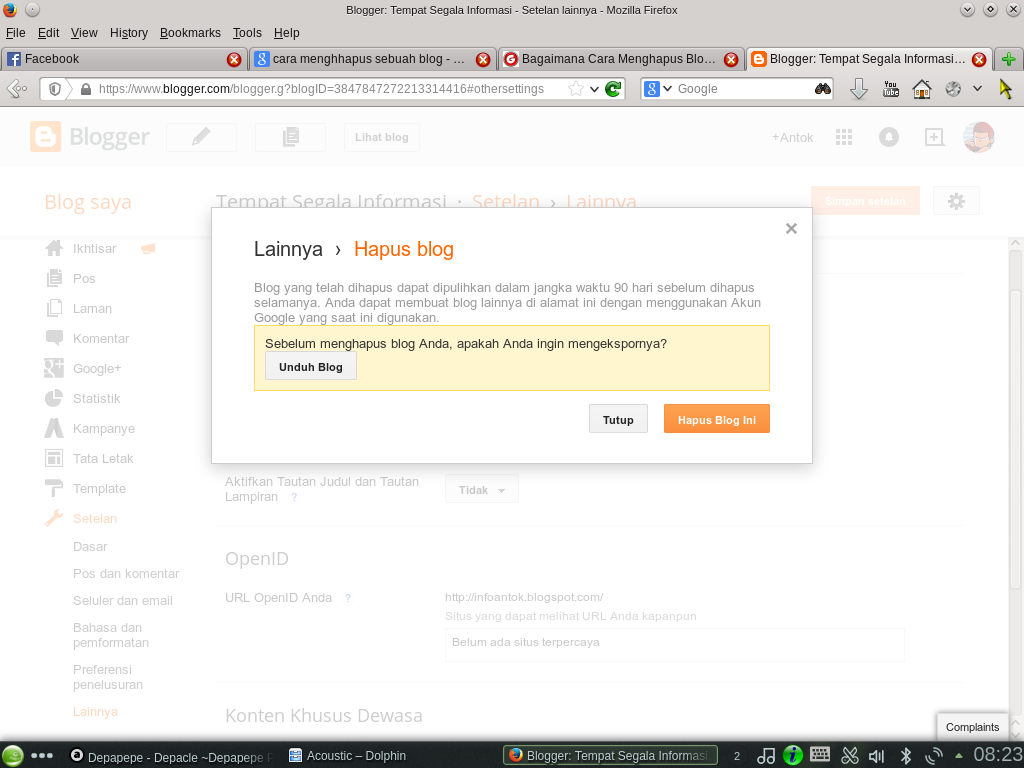
1. Sign in go to the dashboard blog.
2. The dashboard and then point to the drop-down menu select Setelan.
3. Then on the left sidebar, click on Lainnya
4. Then click on the Blog Tools and klik on Hapus Blog
note : Before deleting blog, you can download your blog for another time then the exported by clicking the Unduh Blog. To immediately remove the blog, press Hapus Blog Ini..
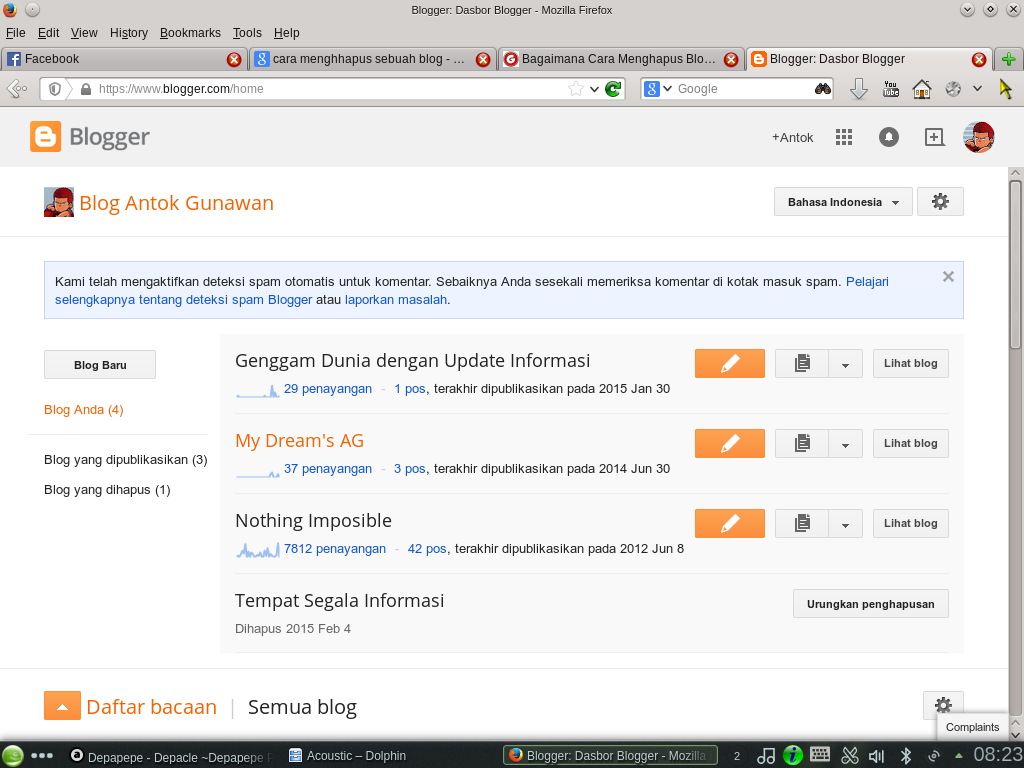
The view that has been deleted
Jumat, 08 Juni 2012
Upload Vulnerability
Upload is process
of transmitting a file from a computer system to other computer
systems. Attacker to upload files to insert in accordance with the
desired command so that it can remotely victim. This attack is
passive as it waits for the victim to take action on a file that is
uploaded.
Minggu, 18 Maret 2012
Magic Number
A magic number or sometimes referred to as a file signature is a number embedded at or near the beginning of a file that indicates its file format (i.e., the type of file it is). magic number can be viewed using a hex editor.
for example, the magic number for JPEG (Joint Photographic Experts Group) image files is 0x4A464946, which is the ASCII equivalent of JFIF (JPEG File Interchange Format). However, JPEG magic numbers are not the first bytes in the file; rather, they begin with the seventh byte.
Similarly, the magic number for image files having the subsequently introduced GIF89a format is 0x474946383961. For both types of GIF (Graphic Interchange Format) files, the magic number occupies the first six bytes of the file. They are then followed by additional general information (i.e., metadata) about the file.
for example, the magic number for JPEG (Joint Photographic Experts Group) image files is 0x4A464946, which is the ASCII equivalent of JFIF (JPEG File Interchange Format). However, JPEG magic numbers are not the first bytes in the file; rather, they begin with the seventh byte.
Similarly, the magic number for image files having the subsequently introduced GIF89a format is 0x474946383961. For both types of GIF (Graphic Interchange Format) files, the magic number occupies the first six bytes of the file. They are then followed by additional general information (i.e., metadata) about the file.
Langganan:
Postingan (Atom)